The New York Attorney General found that about 18 million of the 22 million comments filed in the FCC's 2017 net neutrality proceeding were fake.
Office of the New York State Attorney General, "Fake Comments: How U.S. Companies & Partisans Hack Democracy to Undermine Your Voice", May 6, 2021 (about the 2017 FCC docket)Government
An email address can sign twice.A person can't.
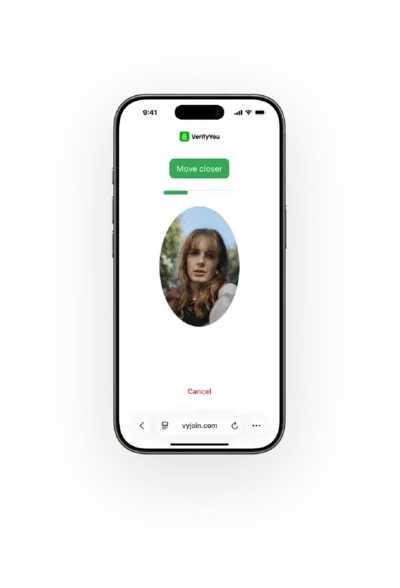
Passive signals check every visitor, and a 3 second selfie, when you choose, confirms a live, unique person is signing or commenting once, with no ID to upload.
The problem
How a petition or comment gets gamed
- J. AlvarezJordan A.j.alvarez@protonSame signer
Duplicate signatures
One person signs again under a new email, and a confirmation link doesn't catch it.
- Public commentDocket 24-109Filed in 0.2sScriptNo face
Bot-flooded comments
Scripts file hundreds of comments to a consultation or docket under made-up names, seconds apart.
- 48 supporters · 17 people31 no person
Astroturfing
A campaign manufactures the look of public support from accounts no real person stands behind.
How it works
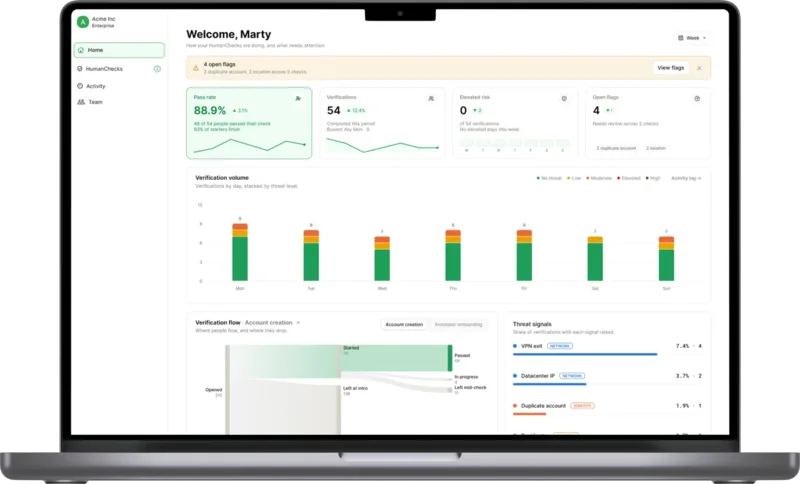
Clean totals, with no friction for real signers.
01
Passive signals score every visitor
Network, device and behavior signals run in the background and build a history for each visitor: past scores and how many submissions they've made today. Scripted traffic stands out early.
02
Risky signers take a face check
When the signals flag risk, a 3 second selfie confirms a live, unique person before the signature or comment is recorded. Good-faith signers never see it.
03
Inside the portal you already use
A one-time passcode, made for one verified face and used once, goes into the petition or consultation platform you already run. With code, it's two API calls.
Comment #4,8126 submissions todayElevated
The platform
Passive defenses first, proof of human when it counts.
Why now
Fake comments have a precedent
Working with major governments.
VerifyYou is SOC 2 Type II and ISO 27001:2022 compliant, and procurement can review the audit before anything launches.
A solution for every scenario
Let's talk trust
Start with a free pilot: see what the check catches on your own users, with no dev work to begin.
With tools like VerifyYou, AI becomes a force for good. It helps prevent AI-driven fraud and can be done with much lower friction than what we built over the years.
Built by humans from
- Quora
- Square
- Gusto
- Cohere Health
- Accenture
Security
Privacy and security in every decision
We keep a face code, not the photo, and hold it under SOC 2 Type II and ISO 27001:2022 compliant controls.
No images stored. VerifyYou does not store images.
No ID or documents. HumanCheck anonymously confirms there is a real, live, unique person, with no name or ID.
A face code, not a photo. We treat it as sensitive biometric data.
 SOC 2 Type II
 ISO 27001:2022
 ISO/IEC 30107-3 PAD Level 1 & 2
 GDPR compliant
Common questions
Does it check whether a signer is eligible, like residency?
No. HumanCheck anonymously confirms a real, unique person signed once. Residency, voter status and any other eligibility rule need their own check, run separately.
Will it slow signers down or hurt completion?
You decide who sees the check and when: at the signature, at the comment, or only for visitors your signals flag. The anonymous HumanCheck is designed to keep drop-off low. A free pilot lets you measure it on your own traffic.
Can it catch someone signing again from a new email or device?
Yes. Recognition is on the face, so a second email or a new phone still matches the signer already on record. Scope uniqueness to one petition or consultation and each person signs once in it. Separately, if a person has been flagged elsewhere in our network, you get an anonymous signal. We never say which platform.
Can it tell a scripted comment from a real person's?
Passive signals flag automated and data center traffic before a comment is ever filed. The face check then confirms a live, unique person submitted it.
What happens to a flagged submission?
Nothing is deleted automatically. Your team reviews flagged signatures and comments in a queue, tags them, and decides case by case, so the call stays yours.
Do you store photos of our users?
No. We keep a face code, not your users' images.
How much work is it to add?
It's two API calls: one to start the check and one to read the result.
Do we have to replace our KYC or bot tools?
No. It sits on top of your stack, so you keep your KYC and bot tools.
What does it cost?
It's 50 to 100 times cheaper than KYC. You pay per check, and nobody uploads an ID document.
Resources
Keep learning
Blog
Congress Wants to Talk About Ticket Bots. But Who's Actually Going to Fix This?
Yesterday the U.S. Senate held a hearing called "Fees Rolled on All Summer Long." Yes, that's a Kid Rock reference.
Read the post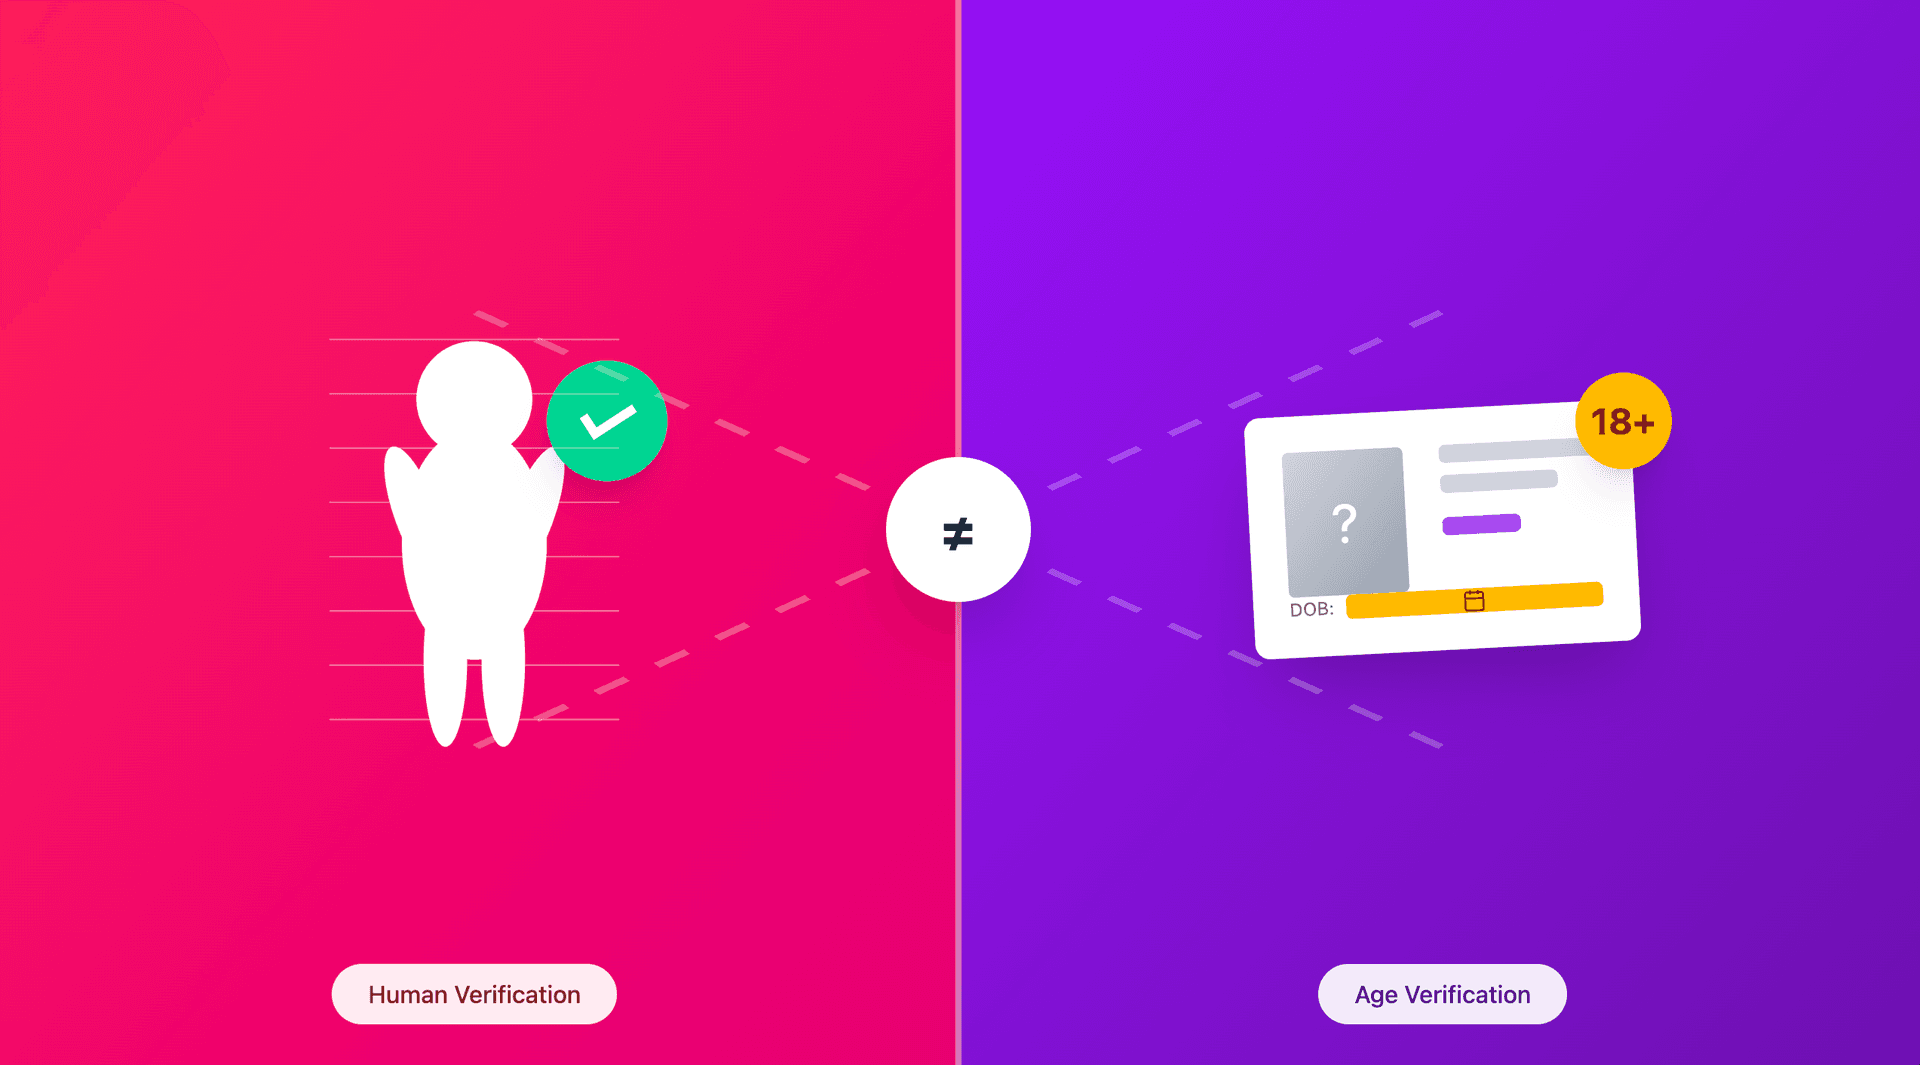
Blog
Human Verification vs. Age Verification: They're Solving Different Problems
Two different questions, two different tools. Conflating them is how you end up with bad policy, annoyed users, and a pile of government IDs stored somewhere you'd rather not think about.
Read the post
Blog
The Best Human Verification Platforms in 2026
Human verification covers four different product categories that solve four different problems. This guide separates them, compares what each one confirms, and shows which published prices vendors actually disclose.
Read the post
Ready to get started?
VerifyYou scales trust: passive signals on every session, a face check only when risk calls for it.